Connexion See the demo

Security questionnaires, answered from your documents. Missing ones, drafted with you.

Your CISO is the bottleneck, and the questions repeat with different wording. Answers are drafted from your policies, certificates and incident records, each citing its page and version, and when no document supports the answer, we help you write it rather than inventing one.

  • Answers from your own evidence
  • Gap analysis before the auditor
  • 25-question library
  • 0 data outside your environment

What is a security questionnaire?

A security questionnaire is an assessment sent by a client, prospect or auditor to verify how a supplier protects information. It covers governance, access control, encryption, subcontractors, business continuity and incident handling, and expects documented evidence behind each answer.

Definition as used on this page. See the glossary.

“Your environment” means your private instance, whichever deployment mode applies: SaaS, private cloud or on-premise.

The scene

A 180-question workbook, and the CISO is in a steering committee all week.

  1. 01Sixty of the questions were answered three times this year, worded differently.
  2. 02The evidence column asks for a document reference and a page.
  3. 03Two answers are eighteen months old and no longer true.
  4. 04One question has no supporting document at all.
  5. 05Sales needs it back on Friday to keep the deal moving.
  6. 06Whatever is sent will be read by the client’s own auditor.

With Optivalue.ai

Seven stages, from workbook received to workbook returned

1 / 7

Connect your sources

Security policies, certificates, penetration test attestations, subcontractor register, continuity plan, incident records. Files stay where they are; the index lives in your private instance.

2 / 7

Indexing, with version history

The librarian agent knows which version of each policy is in force and keeps the superseded ones, which is what prevents quoting a withdrawn control.

3 / 7

Upload the workbook, or open the portal

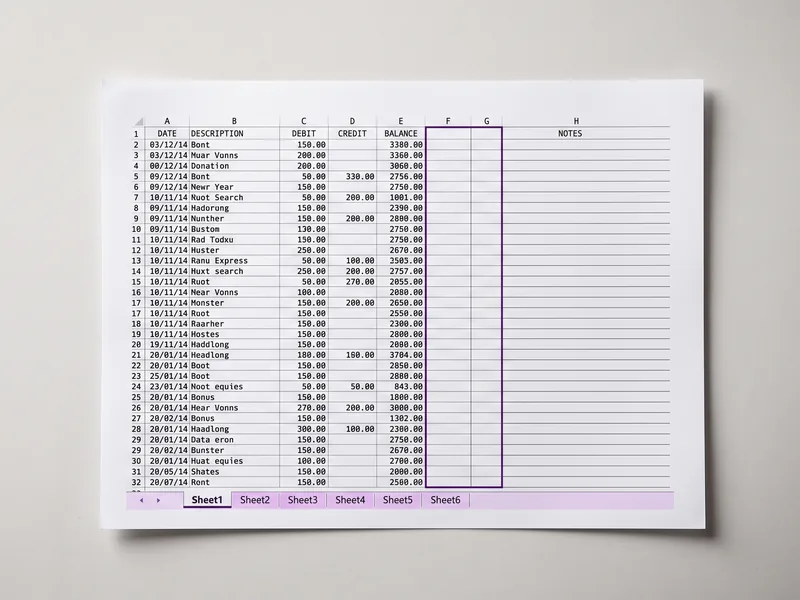
Multi-tab Excel, Word form, standard market questionnaire or assessment portal via the browser extension. The original formatting is preserved.

4 / 7

The security agents answer

Each answer is drafted from your evidence with document, page and version. Questions that need the CISO personally are isolated, so a specialist reviews ten items rather than one hundred and eighty.

5 / 7

Checks, scores and gap analysis

Seven anti-hallucination checks, a 0-to-100 score per answer, and a gap analysis that flags missing, contradictory or out-of-date evidence, before the client’s auditor finds it.

6 / 7

Missing documents drafted with you

Where a policy or procedure does not exist, the gap is declared, an owner named, and the document co-written from your existing material. How that works.

How that works

7 / 7

Named sign-off and export

The CISO approves by name, and the workbook returns in its original formatting with the evidence pack assembled alongside.

The difference

Why a CISO can sign these answers

Compliance is where we come from

We wrote the policies and produced the evidence for large groups under audit. That practice is trained into 72 function agents, 12 sector agents and a librarian, so an ISO or DORA question is handled by an agent that knows what evidence it demands.

How it works
Replayable months later

Source, page, version, score, approver, timestamp, reconstructable when the client audits you next year, which is exactly what an assessor asks for first.

The anatomy of a defensible answer

Your security evidence never leaves

Penetration test findings and incident records are the most sensitive documents you own. Private instance, never shared, jurisdiction of your choice, on-premise available with air-gap support.

Sovereignty in detail

Frameworks move; grids follow

New versions of standards and national transpositions change what assessors expect. Optivalue Watch monitors 193 jurisdictions and updates the assessment grids.

The ecosystem

A general-purpose assistant is fine for an internal summary of a policy. The line is the signature: an assessment returned to a client, whose answers their auditor will test, needs source, version, score and a named approver.

Frequently asked

Security questionnaires: the questions that come up

01

How do you guarantee the AI does not invent answers?

Every claim must trace to a passage in an indexed document of yours, and seven verification checks run before an answer is shown. Where no source exists, the platform declares a gap instead of producing plausible text.

02

What happens when the answer is not in our documents?

The gap is declared, an expert is named, and the missing document can be drafted with you from your existing material. See missing documents.

03

Do we need an answer library first?

No. The platform works on the documents you already have, policies, certificates, records, wherever they live. The repository builds itself as answers are approved.

04

Which frameworks are covered?

Questions referencing ISO/IEC 27001, NIS2, DORA, GDPR and the standard market questionnaires are handled by the security agents. We prepare your answers and evidence; we do not certify or attest compliance.

05

Can our CISO stay in control?

That is the design. The CISO reviews low scores, detected commitments and anything new, then approves by name. Named human sign-off cannot be switched off.

06

Where is our data processed?

In your private instance, never shared, in the jurisdiction you choose, with on-premise and air-gap available. Processing as well as storage. See sovereignty.

Send us the last security questionnaire you filled in by hand.

We run it in front of you, on your documents, in your environment. You will see which answers your evidence supports, and which documents you are missing.

Demo on your documents See the interactive demo